ISO 27001:2022
Information security management: risk assessment, policies, controls and internal audit.
We write the policies and procedures, implement the controls and prepare you for audit, worldwide.
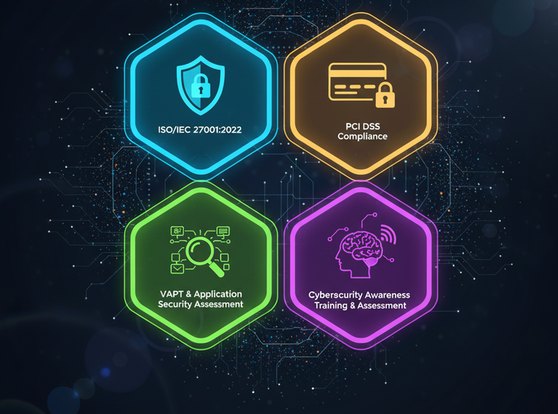
ISO/IEC 27001:2022 and PCI-DSS compliance, VAPT and application security assessment, and cybersecurity awareness training and assessment.
Discuss your certification goal →Information security management: risk assessment, policies, controls and internal audit.
AI management system: responsible AI governance, risk and lifecycle controls.
Security, availability and confidentiality controls with audit-ready evidence.
Protect cardholder data with scoped, tested and documented controls.
Adopt AI with confidence: governance framework, risk and impact assessments and lifecycle controls that stay certifiable.
View the ISO 42001 roadmap →Define boundaries, assets and objectives.
Compare current state against the standard.
Policies, procedures and technical controls.
Internal review and evidence check.
Support through audit and ongoing upkeep.
Tell us about your office, network or compliance goal and get a tailored proposal.
Request a Proposal